When organizations think about strengthening cybersecurity, the first instinct is often to purchase another tool. While security software plays an important role in protecting business systems, adding products without a clear strategy can create new challenges instead of reducing risk.
A stronger security posture is not necessarily built on having the largest collection of tools. It comes from understanding what needs to be protected, ensuring solutions work together, and maintaining visibility across the environment.
Complexity Can Become a Risk
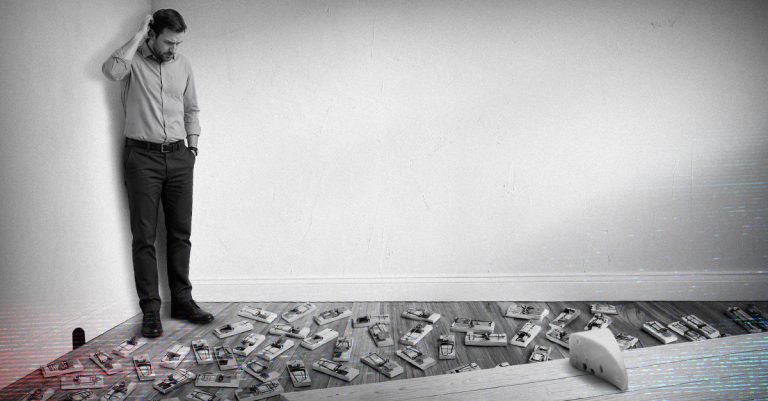
As organizations add endpoint protection, email security, access management, backup, and monitoring platforms over time, security operations can become increasingly difficult to manage. Teams may need to navigate multiple dashboards, compare reports from different systems, and maintain overlapping administrative processes. When visibility is fragmented, identifying security gaps becomes more difficult.
Alert Fatigue Can Conceal Real Threats
Security alerts are valuable only when teams can evaluate and act on them. A large volume of notifications from multiple systems can overwhelm administrators and make prioritization difficult. Over time, important warnings may receive less attention because they appear among countless routine alerts.
Overlapping Solutions Increase Costs
Many organizations discover they are paying for multiple products with similar capabilities. Duplicate functionality can increase licensing expenses while also creating uncertainty about which tool should be trusted during investigations and incident response activities.
Configuration Matters More Than Ownership
A security platform provides value only when it is properly configured, updated, and actively managed. As businesses grow and technology changes, security settings that were appropriate months or years ago may no longer provide adequate coverage. Unused features, outdated policies, and incomplete deployments can leave organizations exposed despite significant investments.
Building a Cybersecurity Strategy That Works
Rather than focusing solely on acquiring additional software, organizations should evaluate how existing tools support their business objectives, security requirements, and risk profile.
- Identify critical business systems and data that require protection.
- Review existing security controls to determine where coverage already exists.
- Reduce unnecessary overlap between products and services.
- Verify that security tools are configured correctly and updated regularly.
- Establish clear monitoring, reporting, and incident response procedures.
The most effective security environment is one where every solution has a clear purpose and contributes to an overall security strategy.
Concerned about insider threats, access control, or AI-related security risks? Contact Nellcom Technologies for a cybersecurity review and learn practical ways to strengthen protection across your organization.